
· 6 min read
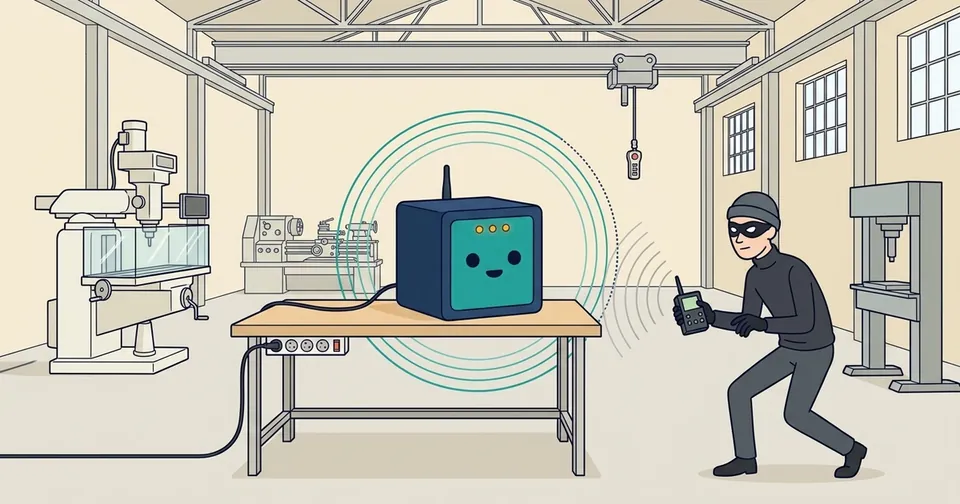
A Wi-Fi Honeypot That Grants Nothing
Against a Flipper Zero that probes, impersonates or forces a disconnect, here is the honeypot that grants nothing, what it sees and what it refuses to do.
Discover how our platform adds assets-based access control to industrial machines and helps businesses comply with NIS2 and Cyber Resilience Act.
· 6 min read
Against a Flipper Zero that probes, impersonates or forces a disconnect, here is the honeypot that grants nothing, what it sees and what it refuses to do.
· 8 min read
Hacked fridges: in October 2026, 700 supermarkets saw their refrigeration supervisors forced into defrost. The facts, and what the debate confused.
· 6 min read
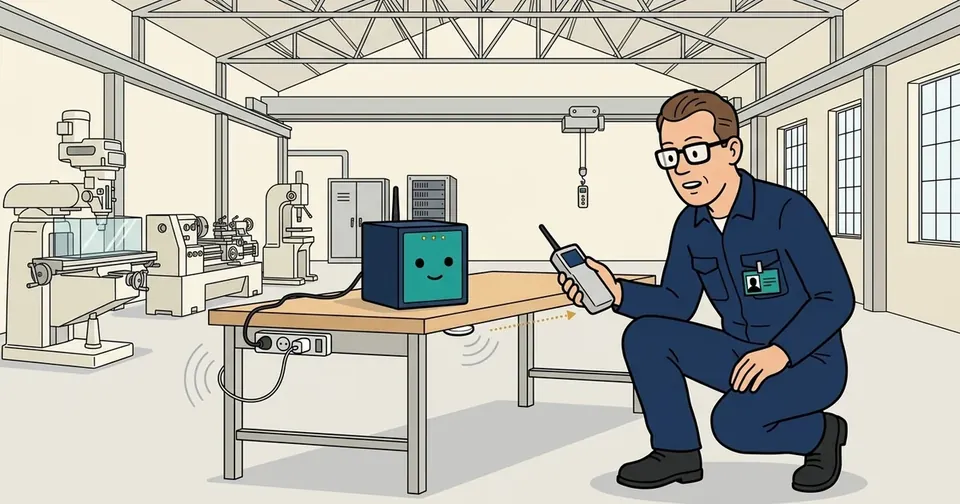
These objects nearly all betray themselves by their emissions, and here is what permanent radio listening detects, what escapes it and what the law allows.
· 5 min read
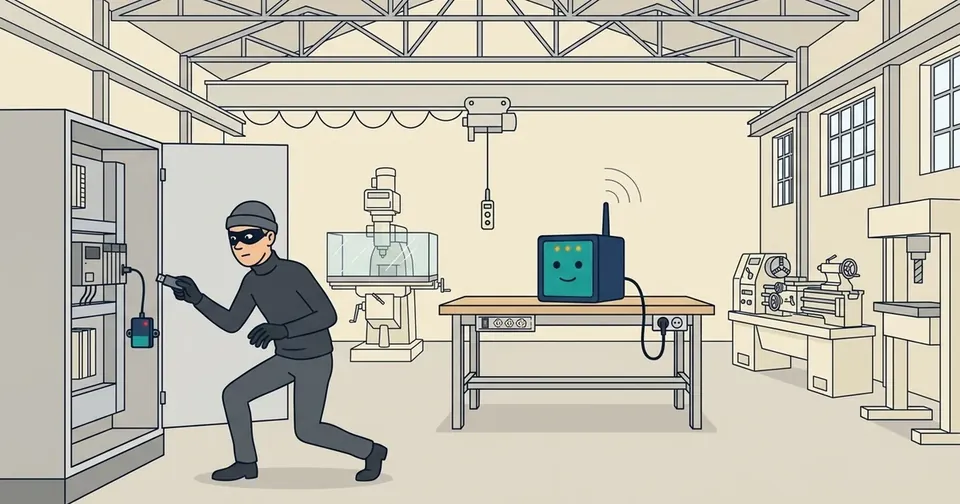
Off the network, USB and serial links are often the only way in and the least watched, and here is what can be done without touching the machine.
· 5 min read
Detecting presence near a machine touches on personal data and on the monitoring of employees, and we set out what to settle before installing anything.
· 10 min read
In shared workshops, fab labs, schools or laboratories, the question of liability comes before security, and that question gave birth to the Cube.
· 7 min read
A proof log that is timestamped, signed and chained can be produced before an auditor or a judge, provided you know exactly what it establishes.
· 7 min read
External contractors are covered by documents that never reach the machine, and we want to bring the rule down to the equipment they actually touch.
· 6 min read
The IEC 62443 standard says little about the person at the machine, and here is where physical access appears in it, what it covers and what it does not.
· 8 min read
Cutting the power to a machine is not an emergency stop, nor a lockout, nor a safety function, and here is what that changes in how we designed the Cube.
· 10 min read
A smart meter measures what a machine consumes but not who was in the room, and here is what the Cube knows by crossing measurement, presence and sensors.
· 6 min read
Securing remote access to industrial equipment and controlling physical access to it are two different problems, and neither one covers the other.
· 9 min read
A technician plugged into a PLC has crossed no firewall and exists at no level of the model, and that Purdue missing link, the person, is our subject.
· 6 min read
IIoT, cloud and remote access bypass the Purdue model, the trade answered with network controls, and one path stays in the Purdue blind spot, the person.
· 6 min read
Is radio monitoring in a workplace legal? Europe treats a hardware address as personal data, the rules differ by country, and here is how we design for it.
· 8 min read
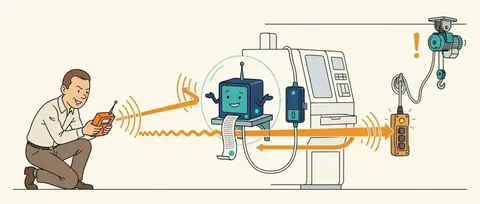
A jammed band and a broken receiver look the same from inside, so we refuse rather than decide blind, and we describe the Flipper Zero as it is.
· 6 min read
An SDR sweeps and misses what transmits while it looks elsewhere, so here is what wideband listening finds in a workshop and what it cannot promise.
· 7 min read
Counting radio addresses is not counting people, and one mechanism decides whether you know who is in the room, for enrolled badges, or track nobody at all.
· 9 min read
Blackout by Marc Elsberg imagined a grid attack in 2012, and we reread the novel that was right about its entry points against the real incidents since.
· 7 min read
The Purdue model sorts industrial systems into six levels, and here is where it comes from, what each level holds and how the standards lean on it.
· 19 min read
The security principles in OT behind a workshop access control system, tested against twelve attacks, with what each mechanism proves and what it does not.
· 8 min read
Why, for the OT retrofit of an industrial machine, we preferred adding units at its boundary to modifying its core, and which building blocks we rely on.
· 5 min read
Part three of our series on IAM at the end of the power cord: what we would do if we led an IAM program, and your IAM vocabulary translated row by row.
· 9 min read
Part two of our series on IAM at the end of the power cord, where five IT reflexes become wrong in OT and where the regulations all end up asking for proof.
· 6 min read
Why your last policy enforcement point is a power outlet, and why IAM at the end of the power cord is where identity and access management is still missing.
· 9 min read
Two EU regulations start applying in 2027 with no transition window, and the 2027 cybersecurity legislation changes what a CE mark on a machine certifies.
· 9 min read
Start with the inventory, then keep walking past the server room, because NIS2 compliance begins where most programmes stop, at the door of the workshop.
· 8 min read
How we actually decide inside Trust-Buster, including the legal and security decision we had to reverse when two European components changed hands.